
A temporary redirect where a permanent one belongs.
Found by Redirect checker →
The URL redirects back to itself and never settles.
Found by Redirect checker →
HTTPS and security headers check
HTTP URLs, mixed content, missing HSTS, insecure forms and subresources, plus a security-headers check for a single URL.
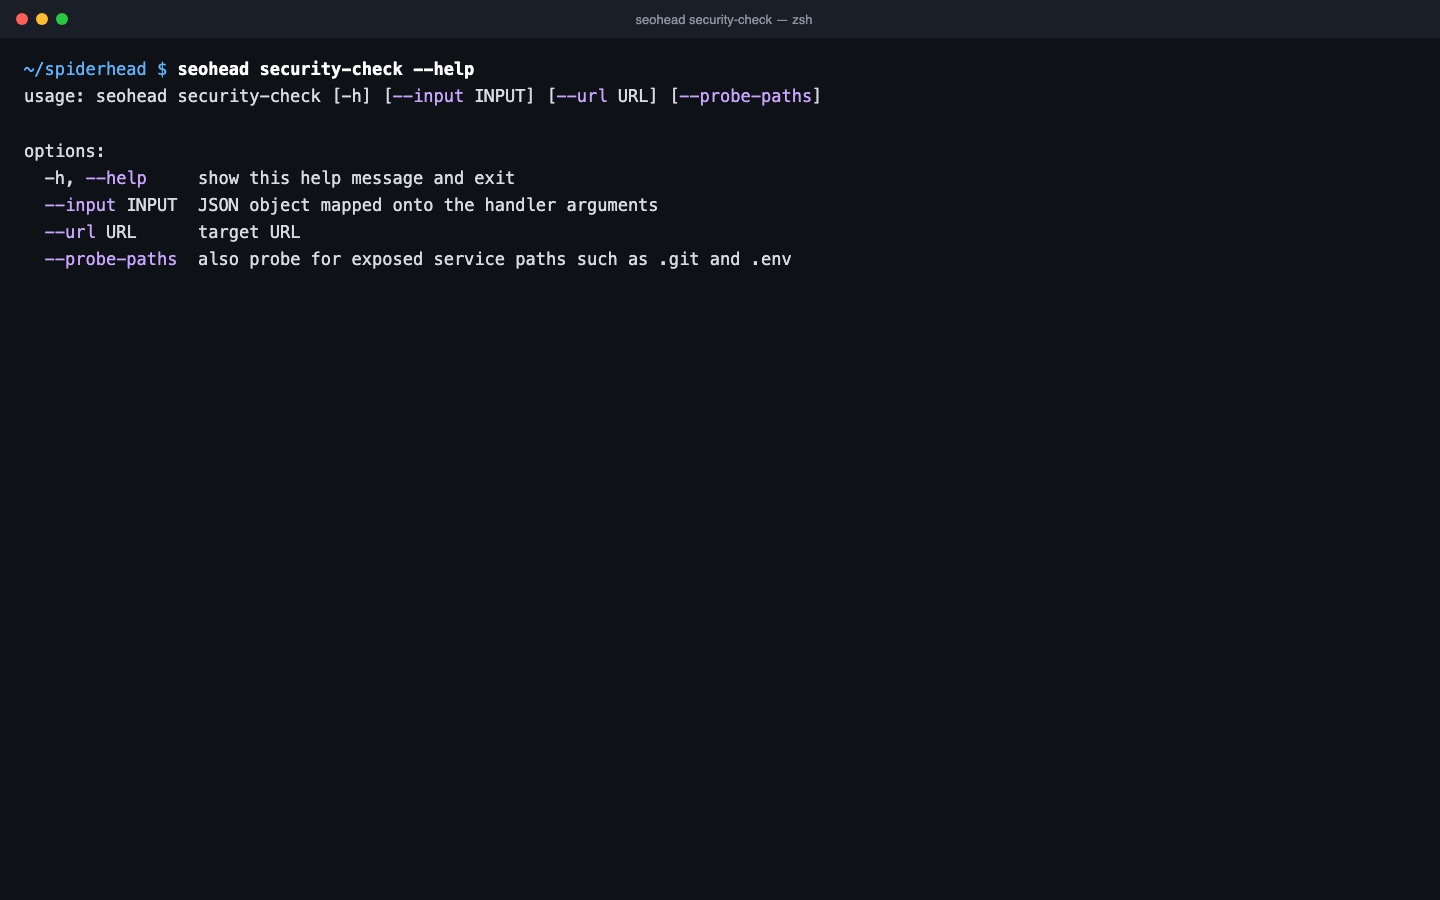
HTTPS and security headers check
Per URL
security-check and headers-check read the response headers of one page.
Across a crawl
Mixed content, insecure forms and http links on https pages are reported per page.
Three steps, one saved scan
Read one URL's response
security-check sends a single GET request and reads the response headers, the cookie flags and the http-to-https redirect.
Score six security headers
HSTS, CSP, X-Content-Type-Options, X-Frame-Options, Referrer-Policy and Permissions-Policy give a 0-100 score and an A-F grade.
Flag mixed content across a crawl
On a crawl, each page is checked for http resources, insecure form targets and missing or repeated security headers.
Checks in this feature
| Check | What it means | Severity | Evidence |
|---|---|---|---|
FORM_URL_INSECURE | A form submits to an http:// action, so the data it sends is not encrypted | Critical | Form action URL on the page |
HTTP_URL | The URL is served over http instead of https | Important | Page URL |
MIXED_CONTENT | An https page loads a resource over http | Important | Page URL and the http resource URL |
INSECURE_SUBRESOURCE | An https page loads an image, script or stylesheet over http | Important | Resource URL and the linking page |
MISSING_HSTS | The page sends no Strict-Transport-Security header | Tip | Response headers of the page |
MISSING_CSP | An HTML page sends no Content-Security-Policy header | Tip | Response headers of the page |
MISSING_X_FRAME_OPTIONS | The page has neither X-Frame-Options nor a CSP frame-ancestors directive | Tip | Response headers of the page |
DUPLICATE_SECURITY_HEADER | A security header is sent more than once on the same response | Tip | Header name and the response that repeats it |
One command
seohead security-check --url https://example.com/Install first: installation guide. Every command also runs as an MCP tool for AI agents.
From the check registry
HTTP_URLMIXED_CONTENTMISSING_HSTSINSECURE_SUBRESOURCEFORM_URL_INSECURE